Mumbai airport: MeitY declares protected systems under IT Act
Eight categories of operational computer systems at Mumbai airport now have protected status under the IT Act, with access subject to written airport authorisation.
In this article
Listen to this article
The Central Government has designated eight categories of operational computer systems at Chhatrapati Shivaji Maharaj International Airport as “protected systems” under the Information Technology Act, 2000, according to a Ministry of Electronics and Information Technology notification. The designation took effect on 23 October 2026, when the notification was published in the Official Gazette.
Notification S.O. 5771(E), dated 22 October 2026, covers computer resources used for airport operations, including airfield lighting, baggage handling, passenger processing and surveillance. It also extends to the computer resources of their associated dependencies, bringing connected supporting resources within the declaration’s scope.
The ministry’s notification sets out who may access these protected systems. Designated airport employees, authorised service-provider personnel and specified outside professionals or officials must have written authorisation from the airport, with additional conditions applying to different groups.
Which airport systems are covered
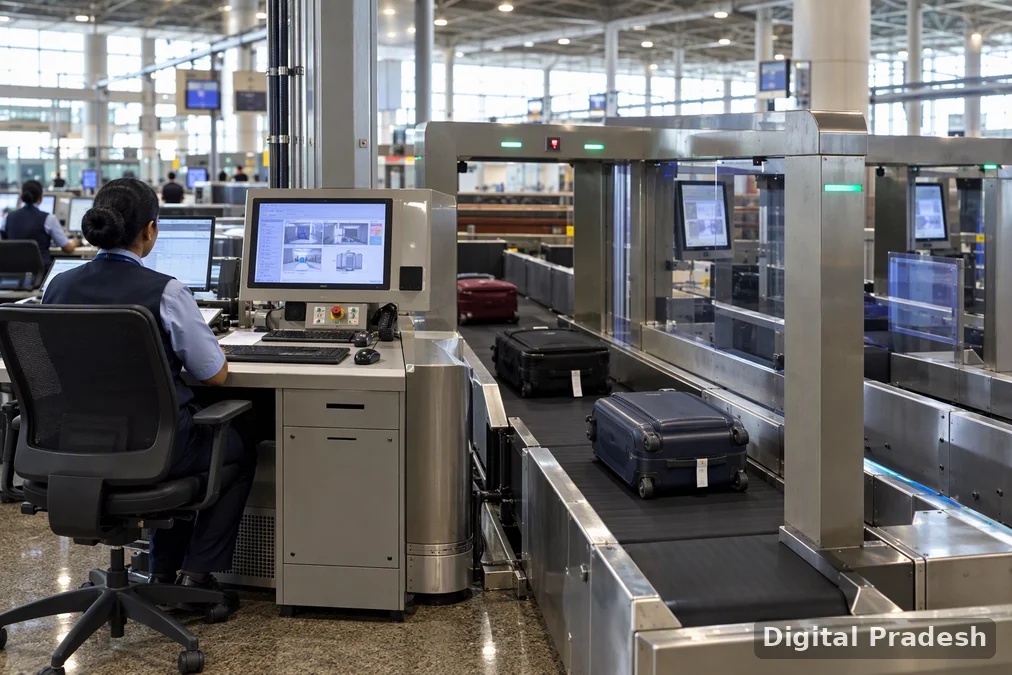
The ministry lists the Airfield Lighting Controlling and Monitoring System, Airport Operation Control Centre and Airport Operations Database among the protected resources. Access Control Systems and Baggage Handling Systems are also included.
Another entry covers Common Use Terminal Equipment, Common Use Passenger Processing Systems and Common Use Self Services. The Closed Circuit Television Monitoring System and Master Clock System complete the list.
The declaration therefore reaches across several operational functions rather than identifying a single database or application. Its wording covers both the listed computer resources and those of their associated dependencies. However, the notification does not provide a separate inventory identifying each supporting resource.
The ministry describes the resources as Critical Information Infrastructure of the airport. This is a statutory classification, not a statement that the systems have suffered a cyberattack. The notification does not identify a security incident, disclose a vulnerability or announce an interruption to airport services.
Nor does it prescribe changes to passenger check-in or baggage procedures. Its operative provisions concern the legal designation of computer resources and the personnel authorised to access them.
Written permission governs access
The ministry’s notification identifies three groups eligible for access, each subject to written approval by Chhatrapati Shivaji Maharaj International Airport.
The first comprises designated airport employees authorised in writing by the airport. Employment alone is not the condition stated in the notification: the employee must also be designated and hold that written authorisation.
The second comprises authorised team members of contractual managed service providers or third-party vendors. These are outside personnel providing services under contract or through a vendor. The notification requires the airport’s written authorisation for their access and expressly limits that authorisation to a need-based basis.
The third includes consultants, regulators, government officials, auditors and stakeholders. For this group, the airport must provide written authorisation on a case-by-case basis.
These provisions distinguish access by employees from access by contractors and other outside personnel. The notification does not give vendors unrestricted access simply because they have a contractual relationship with the airport, or give officials automatic access by virtue of their position. Each category is framed around the airport’s written approval.
The published notification does not name individual authorised users or set out a technical process for issuing credentials. It establishes the categories and approval conditions rather than publishing an operational access register.
What the protected-system designation means
The ministry issued the declaration under Section 70(1) of the Information Technology Act, 2000. That provision supplies the legal authority invoked for placing the identified airport resources within the protected-system framework.
The Department of Financial Services explains that the Act defines Critical Information Infrastructure as a computer resource whose incapacitation or destruction would have a debilitating impact on national security, the economy, public health or safety. In plain terms, the classification concerns the consequences of a resource becoming unusable or being destroyed.
The department’s explanation also distinguishes that concept from the notification process. Under Section 70, the appropriate government may declare a computer resource that directly or indirectly affects Critical Information Infrastructure to be a protected system through publication in the Official Gazette.
For the airport declaration, the commencement clause makes publication decisive: the notification was dated 22 October 2026 but came into force on its Gazette publication date, 23 October 2026. It does not provide a later commencement date or a phased implementation timetable.
National coordination and the operator’s responsibility
The airport notification sits within a broader institutional framework for protecting critical computer infrastructure. In a notification dated 16 January 2014, the Ministry of Communications and Information Technology designated the National Critical Information Infrastructure Protection Centre, or NCIIPC, as the national nodal agency for this purpose under Section 70A of the Act.
The Information Technology (National Critical Information Infrastructure Protection Centre and Manner of Performing Functions and Duties) Rules, 2013, published on 16 January 2014, placed the centre under the administrative control of the National Technical Research Organisation.
Those rules assigned NCIIPC functions including identifying critical infrastructure for government approval and notification, assessing threats, sharing early warnings and assisting with protection plans and standards. They also provided for guidelines, advisories and exchanges of information about incidents and vulnerabilities in coordination with the Indian Computer Emergency Response Team.
The rules distinguish national coordination from responsibility for individual systems. Under their allocation of duties, the basic responsibility for protecting Critical Information Infrastructure lies with the agency operating it.

Please log in to leave a comment.


